Built for regulated institutions from day one
PurpleRail is designed so that no single person and no single system can move money on its own, and every decision leaves evidence.
Six layers between a payment and the money moving
Licensed custody
Crypto-assets sit in an institution-grade custody workspace owned by a licensed financial institution, which sets the transaction policy. PurpleRail operates within it and cannot change it.
Approved destinations only
Funds can only move to addresses and accounts the institution has approved. Refunds go only to screened addresses. Every attempt is checked twice: by PurpleRail and by the custody policy.
Screening on every deposit
Every incoming transfer is screened by a blockchain-analytics provider before funds are released. Sanctioned sources are stopped and frozen automatically and reported.
Two-person approvals
Releasing reviewed payments, changing destinations or limits can require a second operator to approve, with both names recorded.
Self-balancing ledger
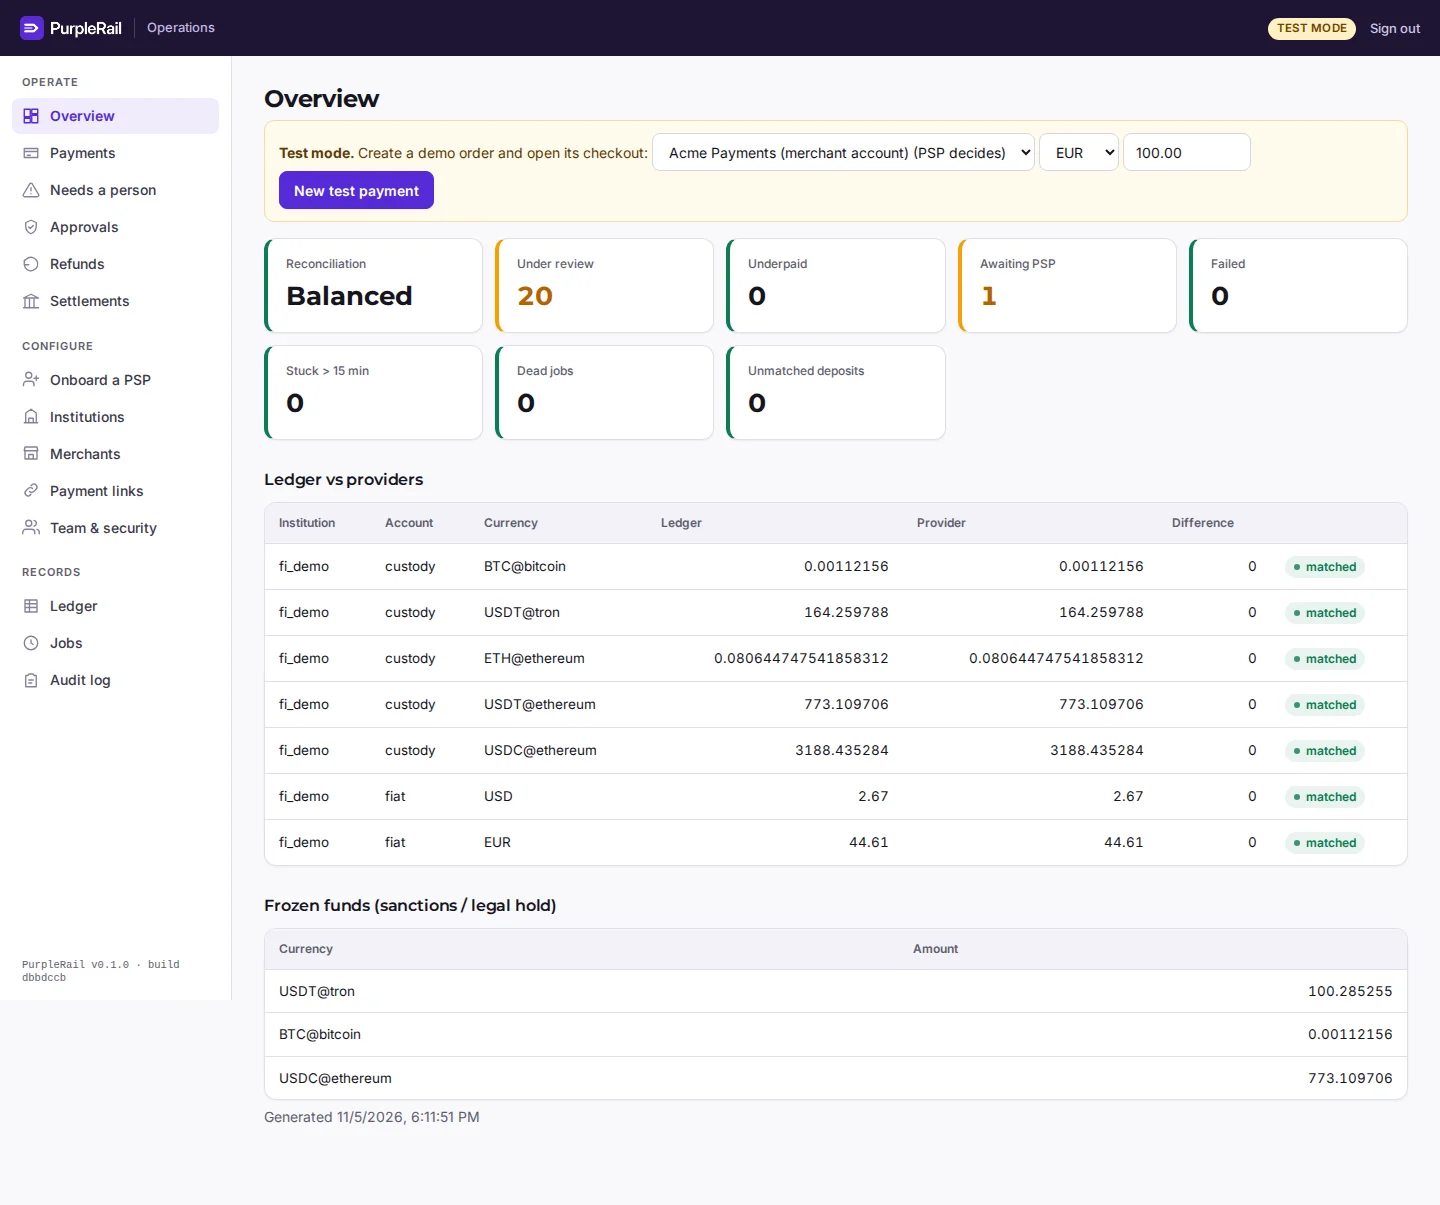
Every movement is a double-entry posting. The database rejects any entry that doesn't balance and any attempt to edit history.
Daily reconciliation
Ledger balances are compared each day with custody and bank balances; any difference is raised for investigation.
Access you can audit
- Role-based operator access: viewer, reviewer, administrator
- Two-factor sign-in for every operator
- Signed, replay-protected webhooks and scoped API keys
- Strict content security policy and no third-party scripts on payment pages
- A complete audit log of who did what, and when
PurpleRail is in private beta. Independent penetration testing is scheduled before go-live.
Privacy by design
Payers don't need to share a name, email or card to pay. We don't sell data or run advertising trackers. Read our privacy policy.